
this post was submitted on 23 Oct 2026
447 points (98.7% liked)
Technology
89924 readers
3483 users here now
This is a most excellent place for technology news and articles.
Our Rules
- Follow the lemmy.world rules.
- Only tech related news or articles.
- Be excellent to each other!
- Mod approved content bots can post up to 10 articles per day.
- Threads asking for personal tech support may be deleted.
- Politics threads may be removed.
- No memes allowed as posts, OK to post as comments.
- Only approved bots from the list below, this includes using AI responses and summaries. To ask if your bot can be added please contact a mod.
- Check for duplicates before posting, duplicates may be removed
- Accounts 7 days and younger will have their posts automatically removed.
Approved Bots
founded 3 years ago
MODERATORS
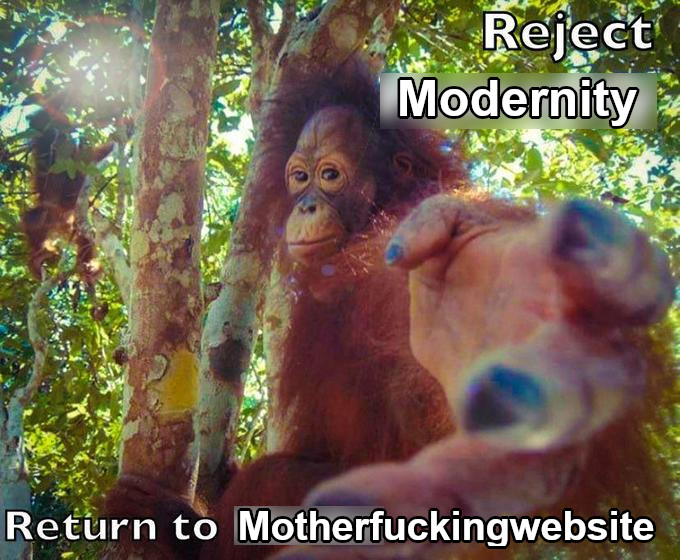
Nothing wrong with static sites!
but what about vulnerabilities in the web server? 😱
Just staple your website to a telephone pole
That would be the best result if everyone just went back to static sites.
load more comments
(1 replies)
Has pure HTML (no css, no javascript) ever had a serious security issue? On the server side obviously not (outside of the apache/nginx/etc. having application bugs), but even on the client side has there ever been an exploit?
I think there's been one or two image decompression exploits over the years, so a site with a malicious file could end up running code on your system. I remember this being an issue with Minecraft clients and player skins at one point, but I can't remember any specific times this happened in browsers tho.
Yeah but if it's just pure HTML you got an ugly-ass website that's annoying to use. There's been many JavaScript and css vulnerabilities over the years of course. But yes there was and still is plain HTML issues
Client side:
- I vaguely remember some base64 embedded encoding malware.
- I do believe there was some issues with early HTML, if you had malformed tags, that could bypass checks and balances.
- Svg, Images, audio, fonts, and video can definitely contain malware. Before you say fonts are a css thing, was a real tag
- IFrames were the worst:
- They had too much power in the past and could hijack the page and browser.
- There was no content security policy back then so they could inject JavaScript into the main page as well.
- Also they can cover the whole screen and present a normal login screen, and hijack all inputs going through it. Think of it like you're on dodgey-site.com and it has a full page IFrame to bank.com. This was a common hack back in the day which inspired an entire http header to help prevent this.
- Anchor tags can link to something dodgey of course.
- Embedded PDFs were a huge issue.
- ActiveX and other web applets was just fucked. They were so bad they caused malware constantly. This is where unsolicited toolbars came from.
- Adobe Flash had many many vulnerabilities over the years.
- Canvas bugs are still a thing today.
Server side, you could execute SQL injection and path traversal just via URL before the page even loads. Malware and other issues can be embedded in text inputs. HTML can be uploaded to the server and in some cases replayed on the page affecting other users (comment sections were infamous for this).
So yeah; a plain HTML page with no JavaScript or css isn't necessarily safe
load more comments
(2 replies)
load more comments
(2 replies)
That's why my site will always be html monke.
How many apocalyptic security flaws can fit into a week?

I never noticed how long the sales guy's hand is
"This bad boy can hold so many limes"
yes
I mean I'll update my Node version, but until someone actually finds an exploit chain on a real system (instead of a vibecoded PoC) I don't see any reason to panic. All these "could"s and "would"s in the article suggest that it's kind of a nothing-burger imo
I'll bet this is another "AI found a known vulnerability so people are making a big deal about it" like the PHP one.
I'm with you on the first part but I believe that 2/4 PHP exploits have been observed in the wild.
If it’s really a PoC, it would actually execute and therefore exploit something (otherwise it wouldn’t be a proof). In which case it doesn’t matter if it’s vibecoded or not. If you succeed in breaching a system with it, there’s an issue that needs to be fixed.
That's exactly the thing. They call themselves PoCs, but most of the time the exploit chain that they "prove" relies on some extremely unrealistic condition, like the intruder already having elevated privileges. Or it's just completely made up and the PoC only "works" because the AI changed the source code. It's incredibly unreliable.
I think you're speaking in general and not about this specific case. This is an unauthenticated remote code exploit. All that needs to happen is your website accepts a brotli from a client or from an external api and tries to read it.
This is a bad one. Broke my no deploys on Friday rule for it.
load more comments
(1 replies)
load more comments
(1 replies)
Who cares if it's vibecoded? The exploit is the exploit.
load more comments
(2 replies)
This what you get for running JS as your back end!
This always struck me as a rather silly idea, to be honest.
Now we've come full circle. I have a vendor who is insisting that I use node.js and pull their code from their NPM repository from the same... For frontend code. Just, have the entire contents of your (their) node_modules folder exposed to the public internet at all times. Isn't this just Javascript with extra steps?
load more comments
(1 replies)
every time the sun rises, shines and sets; a million new node vulnerabilities are discovered
be careful, obviously, but don't let it turn your entire nervous system into pure crystallized cortisol
you can deal with it on Monday
It is kinda funny to hear the manager say "Brotli" as if it were some cursed ancient artefact tho. I'm down to not tell the managers that this is overblown bs. Let them think that we saved the system from certain doom.
load more comments
(1 replies)
Why are people mad? These issues existed and now they don't. It's not like the researchers created them
load more comments
(1 replies)
While the world reels from websites being taken down before critical PHP patches were released
Is it just me or did anyone else not even notice outside of articles lol... It was all resolved by the time I got off work.
It’s not resolved until everyone installs the patch. And there in lies the problem.
An important point yes and I do understand that, but the major players like Steam were updated and done before I knew it. I have no doubt this could come back to bite companies/people lagging behind over the next few years, but the impact to me from websites being taken down was 0, which was my point.
The companies with well-resourced dev teams would have been able to deal with it. But for every one of those there's 50 companies with no dev team who are sending frantic emails to the guy who quit 3 years ago asking if he's available for some urgent work. And another 50 that are not sending any emails because they're oblivious and will get pwned in a few months.
A lot of PHP apps are old, unmaintained or run by people with no idea. That's kinda it's niche.
Yeah but this wasn't an exploit in PHP applications, this was an exploit in PHP.
Our resolution was to unzip a new directory and change the path to PHP in Apache conf
load more comments
(1 replies)
load more comments
(2 replies)
JavaScript should never have been used that way to begin with.
JavaScript should never have been used ~~that way~~ to begin with.
Yeah, so here's the thing. People keep trying to bash on PHP as if anything software isn't manmade and comes baked with flaws that can be exploited. It's the single reason why cybersecurity products are never going to stop being used because no matter what, it's based on something somebody made.
It's going to be flawed or be exploitable by some means. Yesterday it was Log4J, now it's PHP, tomorrow it will be something else. It will never end. Companies deliberately also use this to force you to upgrade because they've abandoned "legacy" products that still work but which they no longer choose to maintain because they want more money and need to stifle you for it somehow.
rihht? opencloud posted a really tacky "nextcloud is dealing with this. checkout open cloud. written in go."
dude... do we need to drop a link to the golang cves? they had a critical bug this year.
ruby? critical regex rce this week.
nodejs? same.
php made the news because of the embargo break making it go viral and everyone loving to hate on php. But people in glass houses should be careful throwing stones.
load more comments
(4 replies)
load more comments
(1 replies)
The sky is falling... Except it isn't. Standard nonsense self advertising. And yes, vulnerabilities exist and canleasd to badness. We agree. It has always been so.
Well, I mean, the AI advances have moved the mean time to exploit between a zero day being announced, and it actively being exploited en masse, from about 3 weeks in 2018, to about -1 day in 2026. So, things have changed a bit.
load more comments
(2 replies)
Imagine working in IT security. How bad a time are you having right now? Are we expecting things to become better or worse the next few months?
When you've been at battle stations for 12 years it just feels like another week.

Open a ticket and add it to the list.

Honestly let it burn.
I am… well sorta. My team has to deal with the cleanup and repercussions at least. Let’s just say this week was not fun. At all.
In addition to the eMudhra certs and the php issue, there were also issues with python, Oracle, Java, and node.js. The certs and php were definitely the highest profile. They shut down incoming traffic to university web servers for the php one. The certs would have been more of a problem if we had extremely short expiration times
load more comments
(2 replies)
Static site suprimacy week.
Node has literally always been like this. It’s just a risk you accept when you choose to use it.
view more: next ›