Hard Pass

9 readers
0 users here now
Rules
  1. Don't be an asshole
  2. Don't make us write more rules.

View hardpass in other ways:

Hardpass.lol is an invite-only Lemmy Instance.
founded 2 years ago
ADMINS

hard pass chief

1


For those unaware, Linus Torvalds this year has deeply cast his lot with the hyperscale LLMs for development of Linux code, dismissing arguments that this is an abdication of responsibility over that code base.

2


Had to evict a big ass spider from my room today and was reminded of this meme template. At least it's easier to evict spiders than cats, the latter don't fit in measuring cups.

3
74
Buckle up! (media.piefed.zip)
submitted 1 hour ago* (last edited 1 hour ago) by inari@piefed.zip to c/memes@lemmy.world
 
 
4
 
 
5
45
submitted 56 minutes ago* (last edited 46 minutes ago) by scaryjelly@sh.itjust.works to c/lemmyshitpost@lemmy.world
 
 
6
7
 
 
8


“I call him Mohamed Al Fayed. And uhhhh— His name is— Abdul, but I think I— call him Mohamed Abdul Al-Sayed.”

This fucking idiot can’t even get the GOP’s infantile smear campaign right. El-Sayed’s full name is ‘Abdulrahman Mohamed El-Sayed,’ and Republicans use that full name as often as possible, because I guess that’s supposed to make him sound more like a terrorist — you know, like that other famous terrorist, Barack Hussein Obama.

But Donny’s too demented to get it right. The name his collapsed cortex shits out instead is ‘Mohamed Al Fayed.’ 

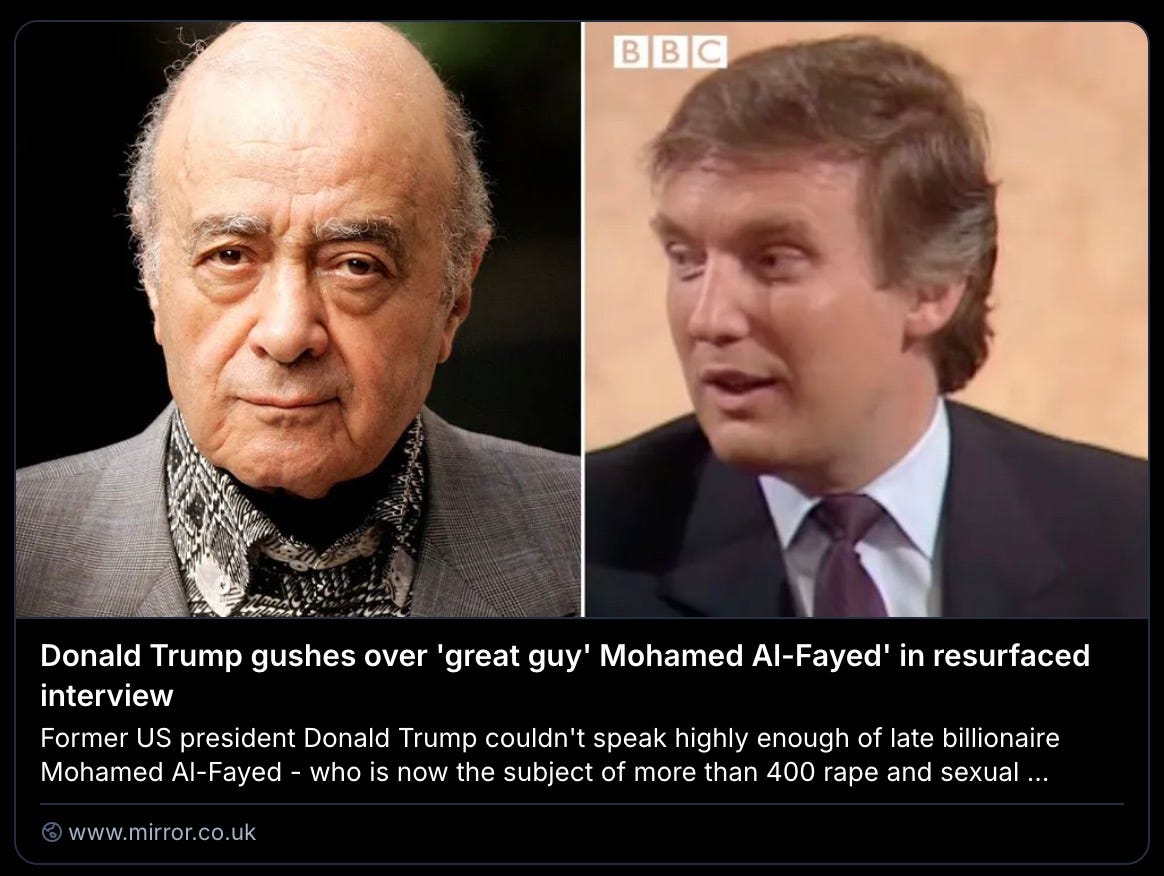
If that name’s familiar, it’s because Mohamed Al Fayed was a billionaire who, during his life, had over one hundred credible rape accusations made against him, his youngest victim being 13 years old at the time. Great guy, right? Well, there was one person who actually thought Al Fayed was a ‘great guy.’

You’ll never guess who it was: Preznit Fuckwit.

Donald Trump gushes over ‘great guy’ Mohamed Al-Fayed’ in resurfaced interview

You know, most of us manage to go through life without having even one dead pedo bestie. Dear Leader has at least two and counting. What a strange coincidence, am I right? Every time we turn around with this guy, new shit comes to light.
via

9
10


Hi selfhosters,

I'm considering improving the security of my homelab/server setup and I'd love to hear some more experienced opinions on my plans.

Like most self-hosters, I started out with a single-server setup: I cobbled together some old hardware, slapped on a NAS-style OS, bolted on Docker and started experimenting. As things go, my setup has grown a lot over the years. I'm running a lot on that machine - NAS capability, local DNS via pihole, a Wireguard VPN endpoint (so I can tunnel into the LAN from outside), many private services (accessible only from inside the LAN), but also some public ones accessible from the open web.

Although I've tried to do my homework in terms of security (various hardening measures for SSH and Docker, reverse proxy, proper SSL termination for everything), I realise I've put a lot of eggs in that one basket and I might want to introduce some network segmentation.

I don't think I'm ready for getting a hardware firewall or a router/switch capable of VLANs just yet. What I'm considering, though, is putting my services available from the open internet on a separate server inside my network - a little Pi 5 I've still got lying around. My idea is that if a container on that is breached and if an attacker manages to escape the container to gain root access, compromise would be limited to the few of publicly available services I have on the Pi, thus limiting blast radius. If combined with (software) firewall rules that make the Pi a 'pariah node' (dropping all incoming connection efforts), lateral movement to other devices on the network could be contained.

An alternative would be to finally make the move to Proxmox. Everything would still be running on one physical machine, but I'd create several VMs: there would be one for private, one for publicly available services, and I'd firewall the latter off rigorously so it cannot connect to anything else.

I'd like your opinion on these plans. Which one would you recommend? Are they both sound, or is there anything I haven't considered? Are there other (easy, non-hardware intense) things I could do to improve security even more?

11
21
commendy (files.catbox.moe)
12


After putting out a nearly three-minute video decrying Trump’s repeated attacks on her Democratic colleague from Minnesota, Jayapal reminded social media users of the president’s “border czar,” Tom Homan, allegedly accepting a bribe in the form of a paper bag stuffed with $50,000 in cash.

...

“If the administration wants to investigate anyone, maybe they should look at themselves first. Anyone remember this?” Jayapal wrote alongside a photo of media coverage that notes Trump’s Department of Justice (DOJ) closed the probe into Homan last year.

Archived at https://web.archive.org/web/20261016192100/https://www.commondreams.org/news/tom-homan-bribe

13


I considered it a fine whine.

14
15
 
 
16
18
euro rule (files.catbox.moe)
submitted 1 hour ago* (last edited 1 hour ago) by blibla@slrpnk.net to c/onehundredninetysix@lemmy.blahaj.zone
17
18
 
 
19


happy spooky season! i already had like 5 pumpkins

20
 
 
21
22


Disgraced music mogul moved to Pennsylvania prison after reports of perks and fight injuries at New Jersey lockup

23
 
 
24
 
 
25


I've had several occasions in my life where I've tried to switch to Linux only to run into hardware incompatibilities that would have taken me man-months to solve. Thanks to GPT my primary personal PC, home media and project server is now running Linux and fully functional. I've got Jellyfin, NextCloud, Navidrome and Joplin all happy. I've also been able to wipe an obsolete MacOS off my 2017-era Macbook Pro and it's happily running Mint.

There's a deep irony in Windows being enshittified by AI, while the same AI makes Linux about a billion times more usable. Now I have a leftover Windows micro-PC running a local LLM model, so I can be less dependent on GPT, as long as time isn't a factor...

view more: next ›